Detecting financial fraud with Neo4j
Online insurance applications generate a trail of events—submissions, underwriting decisions, payments—each tagged with an IP address. By enriching these events with Fastah IP geolocation and loading them into Neo4j, you can detect fraud patterns that tabular data would hide.
This guide extends Neo4j's fraud detection documentation by adding privacy-safe geographic attributes to application events. When submission and payment originate from distant locations—or cluster with known bad actors—you can trigger a human review.

The fraud pattern
Each insurance application generates events with IP addresses:
applicationSubmitted— applicant submits from IP address ApaymentMade— payment arrives from IP address B
If the distance between A and B exceeds a threshold (e.g., 500 km), flag for review.
Event schema:
Load geolocated events into Neo4j
This Cypher query ingests Fastah API responses, creates IPAddress nodes with spatial points, and links them to Application nodes:
In production, stream events from your application or ETL pipeline rather than hard-coding them.
Detect suspicious applications
Find applications where submission and payment IPs sit far apart:
The point.distance() function returns meters, so we divide by 1000 for kilometers.
Visualize with Neo4j Bloom
Use Neo4j Bloom to explore relationships between applications and shared IP addresses:
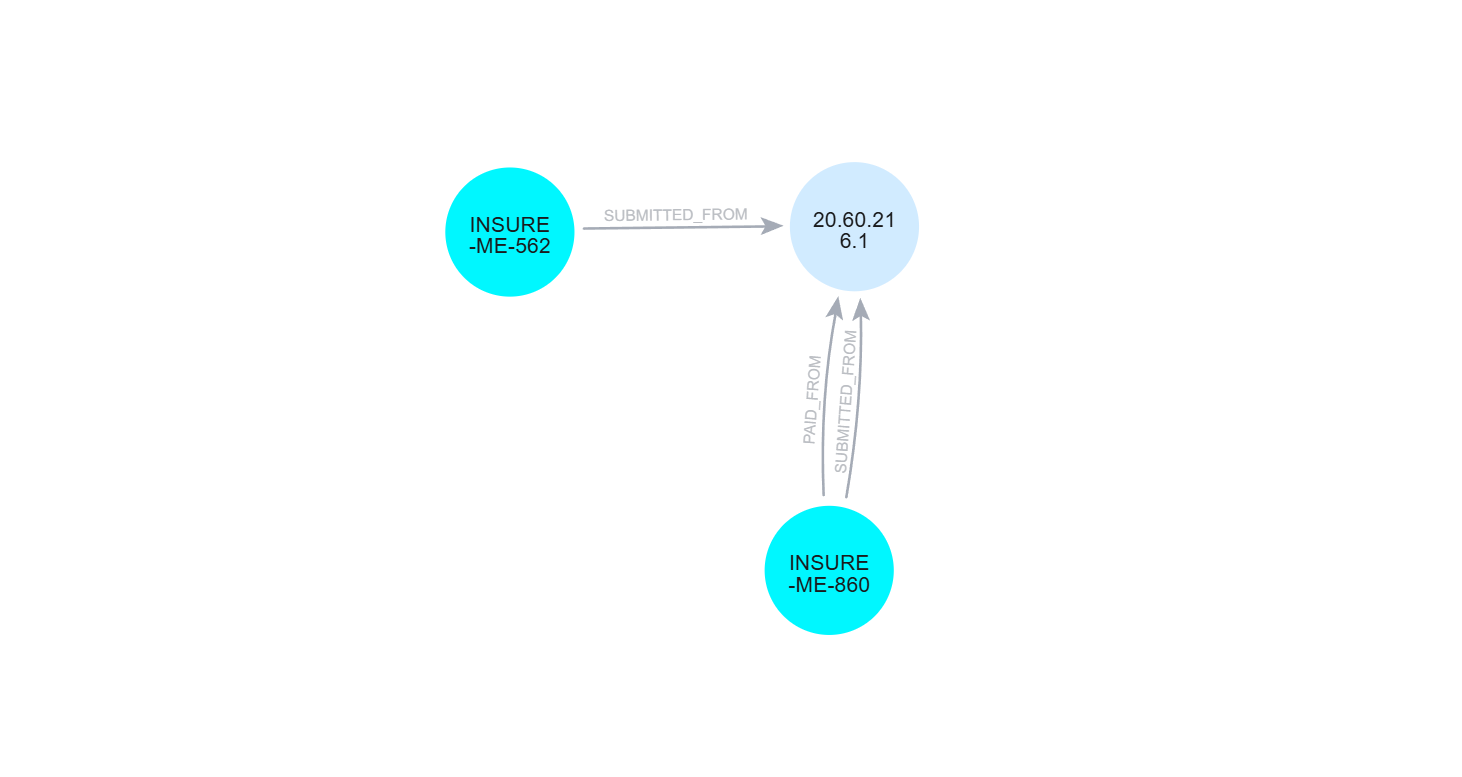
Neo4j's graph structure reveals patterns you'd miss in tabular data—such as fraud rings where multiple applications share IP addresses, or account takeovers where submission and payment originate from different continents.